
Build on Amazon Bedrock AgentCore
Deploy your agents, restrict tool access through Gateway and retain incident context. Review execution traces to understand agent decisions.
Applied AI for security operations
Build and operate AI agents for your SOC.
Turn security alerts into evidence-backed investigations and controlled response workflows. In five hands-on days, build, orchestrate and evaluate SOC agents with security context, analyst handoffs and governed response.
$4,599 USD per seat Labs, models and course code included
Enrolling a full team? Contact us
Accelerated fictional lab demonstration. An analyst directs AI agents to investigate, hunt, contain, remediate and verify recovery across Microsoft Defender, CrowdStrike Falcon and SentinelOne. Changes require analyst approval. Model and EDR communications are simulated.
Course technology
Build on AWS. Connect your agents to the evidence and response tools in your SOC.

Anthropic · Claude models
OpenAI · GPT models
Open-weight models

Amazon Bedrock AgentCore
Core labs use Microsoft Defender and CrowdStrike Falcon. Adapt the integration patterns to other EDR APIs.
Core lab
Core lab
Build a working SOC workflow, a tested evaluation suite and a practical plan for introducing agents into your security operation.
Connect security tools, orchestrate specialist agents, retrieve relevant context and execute approved responses. Build one connected project throughout the week, then measure its accuracy, failure modes and operating cost. Analysts supervise decisions and response permissions stay explicit.
Beyond the classroom
Estimate potential time savings
This estimate uses example inputs. Replace them with your alert volume and measured time savings, including review time, before using the result to plan a SOC pilot.
Build. Run. Review.
We provide the lab, cloud infrastructure and model access. Run controlled attacks in an isolated environment, then use your agents to investigate, plan and carry out an approved response.
30 days of continued lab accessKeep practicing after the course. Your agent code is yours to keep.
Build a team of collaborating AI agents
Learn to build agents that share evidence, refine each other’s findings and move cases through triage, contextual retrieval, hunting and analyst-approved response.
Connect your tools
Defender
Falcon
Threat evidence inApproved actions out
Defender + Falcon core labs
Shared evidence & context
Builds the incident picture
Finds related activity
Retrieves cited security context
Proposes governed actions
Choose your models
Anthropic · Claude
OpenAI · GPT
Open-weight models
Agents exchange evidence, findings and response recommendations.
Where your agents run together
Build, connect and run your agent team on AWS.
Hands-on in AI-CyberRangeX.
Learn an approach you can adapt to other security platforms.
Deploy your agents, restrict tool access through Gateway and retain incident context. Review execution traces to understand agent decisions.
Work with Microsoft Defender and CrowdStrike Falcon alerts, evidence and response APIs. Set permissions and require approval before containment.
Evaluate orchestration, retrieval, analyst handoffs and approved response against labeled cases. Compare Anthropic, OpenAI and open-weight models for quality, latency, cost and data handling.
The learning path
One connected SOC project across five days: connect, orchestrate, ground, govern and evaluate. Keep the code and operational evidence.
Day 01 8 hours
Build a Python agent on Amazon Bedrock AgentCore with structured outputs, evidence references and scoped tool access. Connect SIEM/EDR/XDR and threat-intelligence patterns through REST APIs and webhooks. Microsoft Defender and CrowdStrike Falcon are the core EDR labs; additional systems use labeled fixtures or adapters.
Build a triage agent that retrieves an alert, gathers evidence and produces a sourced disposition. Validate tool inputs and deny access outside its case scope.
Python triage agent, tool schemas, scoped connectors and evidence-linked output.
Day 02 8 hours
Translate analyst procedures into explicit workflow graphs. Combine deterministic steps with agent reasoning and route work between triage, investigation and hunting agents. Manage case state, bounded retries, stopping conditions and specialist handoffs.
Build an orchestrated investigation for a phishing-to-endpoint case. Correlate alerts, delegate evidence collection and a hunt, then assemble a case narrative. Test a failed tool and an inconclusive branch.
Workflow graph, specialist agents, shared case schema and execution traces.
Day 03 8 hours
Build retrieval-augmented generation over runbooks, asset and network context, threat intelligence and historical incidents. Practice chunking, embeddings, metadata filters and citations. Enforce case and tenant boundaries, freshness and evidence provenance. Use malware findings and detection queries as supporting investigation tools.
Build a security knowledge collection and retrieve relevant context for an investigation. Compare retrieval with and without metadata filters, reject stale or unrelated evidence and test a poisoned document.
Retrieval pipeline, context corpus, citation checks and retrieval evaluation cases.
Day 04 8 hours
Build review, revision, rejection and escalation paths for analysts. Separate evidence from instructions and enforce permissions outside the model. Test prompt injection, data poisoning and tool abuse. Require scoped approval for response, verify results and handle retries without duplicate actions.
Present an evidence-backed response proposal to an analyst. Test approve, revise and reject paths, malicious retrieved instructions, cross-case access and a timed-out action. Verify approved containment only inside the range.
Analyst handoff, approval policy, adversarial tests and response audit trail.
Day 05 8 hours
Benchmark commercial and open-weight models on the same labeled cases. Measure investigation correctness, retrieval quality, unsupported claims, escalation quality, context usage, latency and cost. Inspect traces, establish regression gates and plan a monitored enterprise pilot.
Run the full agent workflow on held-out cases. Compare model and context strategies, diagnose failures and present the capstone with evaluation evidence, operational ownership and staged rollout criteria.
Evaluation suite, model scorecard, capstone, operational runbook and pilot plan.
Keep the code, workflows and evidence you create during the course.
Keep the triage and investigation agents, scoped tool definitions, evidence references and analyst handoff templates you build.
Keep workflow graphs, specialist-agent routing, case state, bounded retries and investigation traces.
Keep the security RAG pipeline, training corpus, metadata filters, citation checks and case templates that distinguish facts from uncertainty.
Keep approval rules, response verification, duplicate-action prevention and recovery exercises for controlled containment.
Compare evidence accuracy, missed threats, escalation quality, latency and cost using labeled cases and model scorecards.
Define monitoring, data boundaries, permissions, rollout gates and accountable owners using your capstone results.
Your role. Your outcomes.
For SOC analysts, incident responders, threat hunters, detection engineers and security architects.
Build agents that investigate alerts, hunt threats and identify affected systems.
Build security RAG and orchestrated playbooks with analyst handoffs and approved response.
Evaluate agent accuracy and safety, and keep your code to adapt for your SOC.
Before you attend
You need SOC investigation knowledge and basic Python for the build labs. We teach the AWS and AI agent foundations you will use.
For CISOs, security executives, SOC managers and leaders responsible for SOC operations.
Identify where agents can support response and where human judgment is essential.
Define access limits, approval steps and accountability for agent decisions.
Assess model quality, cost and risk using lab results before planning a SOC pilot.
Before you attend
Work through guided and paired labs to review agent findings and approve response actions. Basic Python is required to build the agents independently.
For students pursuing a bachelor's or master's degree in cybersecurity who want to turn academic foundations into practical SOC skills.
Apply incident response theory to guided investigations and controlled attacks in AI-CyberRangeX.
Build and keep your own AI agents, code and lab results for portfolio projects or further research.
Evaluate model accuracy, investigate threats and test guardrails and human approval workflows.
Before you attend
Bring basic Python and a working understanding of networks, operating systems and incident investigation. Relevant coursework and practical labs can provide this foundation.
Cross-domain experience
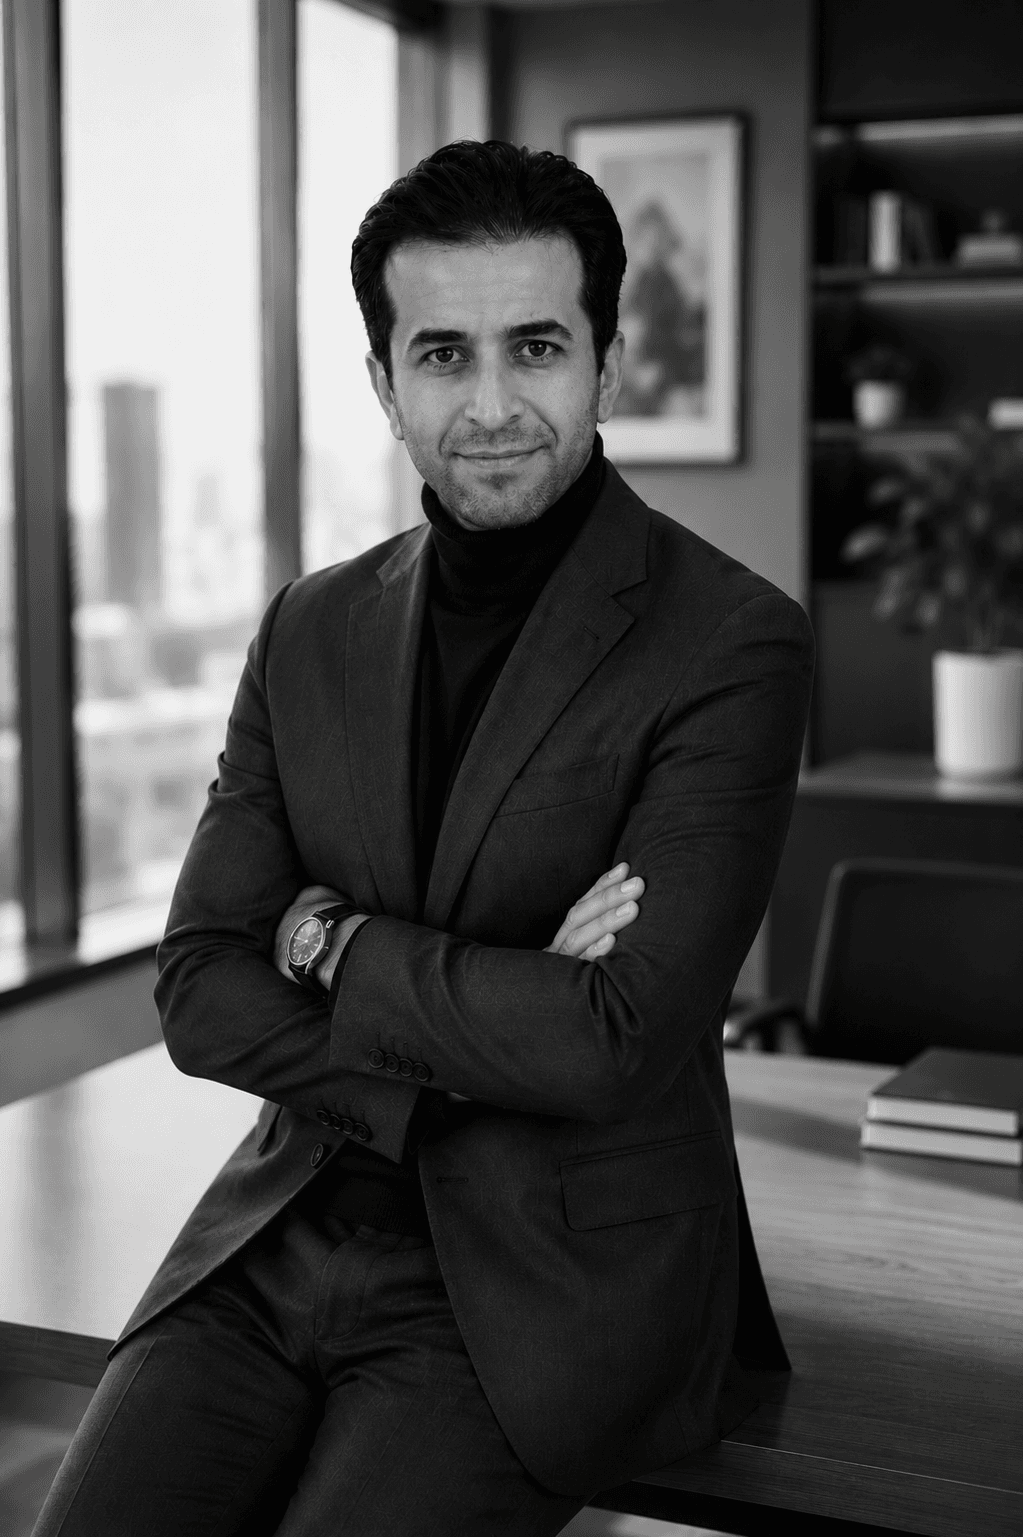
Anwer Gertani brings cross-domain experience spanning security operations, incident response, malware reverse engineering, threat research and AI automation. At Deloitte since 2019, he has progressed from senior malware reverse engineer to Senior Manager, leading teams working across malware analysis, incident response and threat intelligence.
His work focuses on implementing AI agents in large enterprise environments, from detection agents and automated malware analysis to coordinated incident response. He combines threat research with research automation, building tools and analysis pipelines that turn adversary behavior into actionable evidence. He brings that experience into the classroom to help students build, integrate and govern agents for their own SOC.
Build and integrate agents for investigation, analysis and approved response.
Connect adversary behavior, malware findings and threat intelligence.
Build repeatable analysis pipelines that turn research into evidence for response.
20 upcoming course dates across 15 cities in 2027. Join live online or request in-person attendance at the host city’s hours.
* In-person delivery: In-person training is offered only when at least 10 participants choose in-person attendance for the same cohort. Apsispoint will confirm the delivery format before you make travel arrangements.
Join any cohort live online at the host city's hours, with the same instructor, guided exercises and lab access.
Use your team pack across several 2027 dates to maintain SOC coverage while colleagues attend.
Train up to 20 participants on your working week, on your premises or in your AWS tenant, with scenarios drawn from your environment.
20 course dates · $4,599 per seat · Live online or confirmed in-person delivery
Repeat the exercises with lab access for 30 days after the course. Virtual participants attend live at the local times shown.
Make the case to attend
Everything you need to plan your training and secure approval.
Use the code, evaluation templates and pilot plan you create during the course to guide this work.
Find the details on experience, lab access, delivery and what you take home.
SOC analysts, incident responders, engineers and cybersecurity bachelor's and master's students build and test the agents. For the build labs, you need basic Python and familiarity with incident investigations, gained through work, coursework or practical labs. Students apply their academic knowledge to SOC exercises and keep their code for portfolio projects or further research. Executives and SOC leaders join paired labs to assess findings, set approval rules and decide how to evaluate a pilot. All participants work through the same incident exercises and final review.
You will build a connected workflow for triage, investigation, security RAG, multi-agent orchestration and governed response. Maintain evidence-linked case records, test analyst handoffs and evaluate agents on malicious and benign cases. Keep your code, workflow graphs, retrieval pipelines, evaluation fixtures, policies, operational runbook and SOC pilot plan. Malware sandbox findings support investigations rather than forming a separate specialization.
Yes. The labs cover Microsoft Defender for Endpoint / Defender XDR and CrowdStrike Falcon. You retrieve investigation data, configure permissions and use supported response actions. You learn the authentication, data formats and capabilities of each integration. Response actions run only in the lab through the approval controls you build.
You build on Amazon Bedrock AgentCore and compare models from Anthropic and OpenAI with open-weight models on the same labeled SOC tasks. You assess evidence quality, latency, cost and data handling, then learn how to adapt an open-weight workflow for your own environment. Deployment, tool access and logging determine the data boundaries. We provide model access and the AWS environment; no prior AI or AWS experience is required.
No. Bring a laptop with a modern browser. We provide AI-CyberRangeX, AWS and model access, with no personal API keys or cloud bill. Public cohorts use synthetic or anonymized cases, so you do not need company data. Attack simulations and malware analysis stay inside the isolated range. You keep lab access for 30 days after the course; the environment is then removed. Private-cohort data and deployment boundaries are agreed during scoping.
Microsoft Defender and CrowdStrike Falcon remain the core EDR labs. Additional SIEM, identity, email and ticketing examples use labeled training fixtures or adapters. Platform logos describe transferable integration patterns, not a promise of a dedicated live environment for every vendor.
The capstone assesses evidence accuracy, retrieval quality, orchestration, appropriate escalation, approval enforcement, recovery from failures and operational reporting. You compare models on the same labeled cases and document limitations. This is practical professional development, not a job-placement guarantee or a substitute for production experience.
Yes. A team pack can be split across public 2027 dates. Any cohort can be attended virtually at the host city's hours. Private cohorts can be scoped around your working week and environment, with delivery agreed in advance. Lab access continues for 30 days after the course so participants can repeat the exercises.
In-person training is offered only when at least 10 participants choose in-person attendance for the same cohort. Apsispoint will confirm the delivery format before you make travel arrangements.
Within five business days, you receive participant skills reports, the final exercise scorecard, the agent and policy repository, and certificates with 40 CPE credits per participant. Your team also leaves with a SOC pilot plan covering the use case, model choice, data boundaries, approval owners and success measures. Participants have 30 more days of lab access to test changes.
Choose a public course date and ask about seats. When online checkout is available, you can also pay by card or US ACH bank debit. For a full team or private cohort, use the Contact us link to send a training inquiry. An advisor will discuss your group size, preferred format and dates within one business day. Purchase orders, company invoicing and vendor onboarding documents are available on request.
Transfer your seat to a later cohort or a colleague at no charge up to seven days before the first day. Cancel 14 or more days before the first day for a full refund. If you leave before the end of day one, your seat is refunded in full under the first-day guarantee. A private cohort can be rescheduled once at no charge with 14 days' notice.
Choose your course date and ask about seats. Your lab, model access and course code are included.
Enrolling a full team? Contact us
Individual and group bookings
Send your course inquiry and we will help with availability and company invoicing.